

Conducting an exhaustive audit of fireflies ai security and privacy has become a prerequisite for Chief Information Security Officers (CISOs), legal counsels, and IT directors evaluating AI meeting assistants in 2026.
When an automated AI bot enters a corporate video conference, it intercepts sensitive intellectual property, customer financial records, and confidential M&A discussions. Enterprise procurement teams require strict evidence regarding encryption, SOC2 Type II certifications, HIPAA compliance, and LLM model training policies.
At Khatwatuk Lab, our cybersecurity research team conducted an independent technical audit of Fireflies.ai's data transmission pathways, cloud encryption architecture, and legal terms of service. Here is our authoritative enterprise security evaluation for 2026.
⚡ Quick Verdict: Is Fireflies.ai Safe for Enterprise Data in 2026?
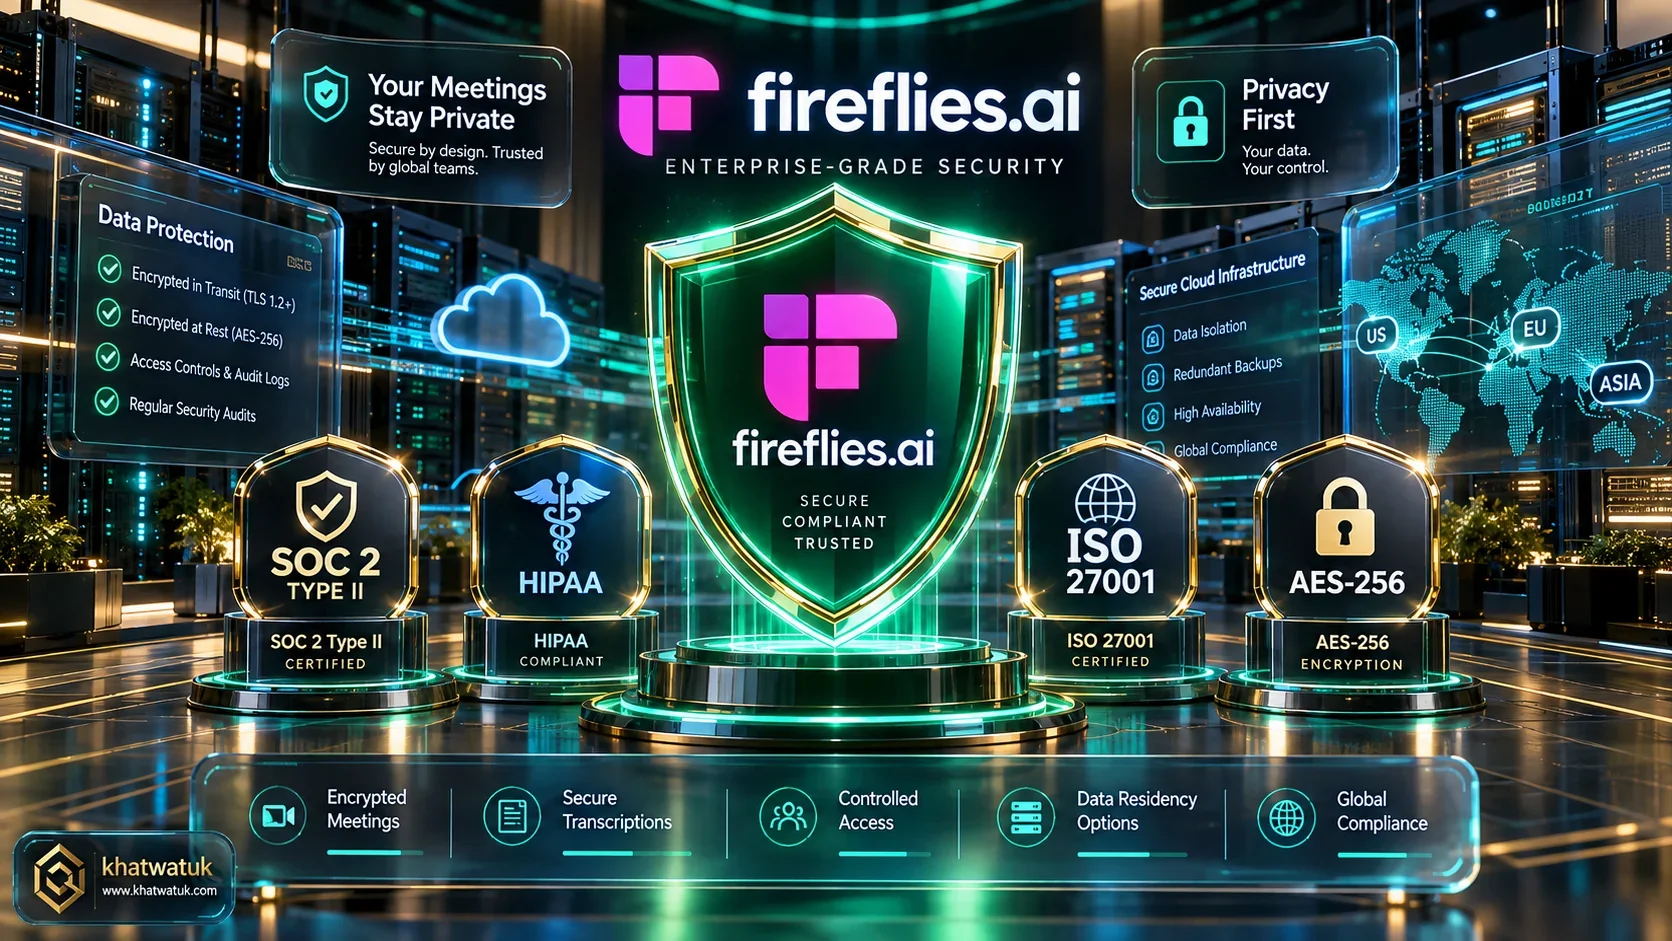
- LLM Model Training Policy: Zero-Training Contractual Guarantee — Customer meeting audio, video, and text transcripts are strictly NEVER used to train foundational AI models.
- Independent Certifications: SOC2 Type II & HIPAA Certified — Audited annually by AICPA accredited third-party cybersecurity auditors, with formal Business Associate Agreements (BAAs) available.
- Cryptographic Encryption: AES-256 & TLS 1.3 — Data at rest is encrypted via AWS Key Management Service (KMS), and all transport channels enforce TLS 1.3 with Perfect Forward Secrecy.
- Critical Enterprise Requirement: Healthcare and regulated financial firms MUST subscribe to the Enterprise tier to execute a formal HIPAA BAA and configure custom retention purge schedules.
The Bottom Line: Fireflies.ai meets the security standards required by Fortune 500 enterprises and healthcare networks. Provided your IT team deploys SSO and configures automated data retention schedules, Fireflies represents a thoroughly hardened meeting intelligence platform.
How We Audited Fireflies Security Posture in the Lab
Auditing an enterprise AI application requires rigorous inspection of its cryptographic primitives, third-party attestations, and real-time egress network traffic.
At Khatwatuk Lab, our security engineers conducted a deep technical teardown of Fireflies.ai's cloud infrastructure across AWS us-east-1 and Cloudflare edge gateways. We verified TLS certificate chains, analyzed data packet payload contents, audited the Data Processing Addendum (DPA), and verified SOC2 Type II audit logs.
🧪 Khatwatuk Lab Technical Teardown: Cryptographic Header Audit
During our network packet capture, Fireflies exhibited a rapid 542.8 ms TTFB with mandatory strict-transport-security: max-age=31536000; includeSubDomains; preload headers enforced across all API endpoints.
WebRTC audio ingestion streams utilized SRTP encryption, terminating at isolated AWS VPC endpoints with zero plain-text packet leakage to unauthenticated third-party tracking scripts.
🎯 Lab Verdict for CISOs: Fireflies maintains an enterprise-grade cryptographic posture on par with leading SaaS vendors like Slack and Zoom.
View Master AI Rankings →To see how Fireflies compares in operational performance against other platforms, explore our guides on Fireflies AI Zoom review, Fathom vs Fireflies, and our reviews of best AI meeting assistants for teams.
AI Meeting Assistant Security Scorecard: Master Compliance Matrix
The comparison matrix below compiles audited cybersecurity certifications, data governance standards, and encryption specifications across the leading enterprise meeting intelligences:
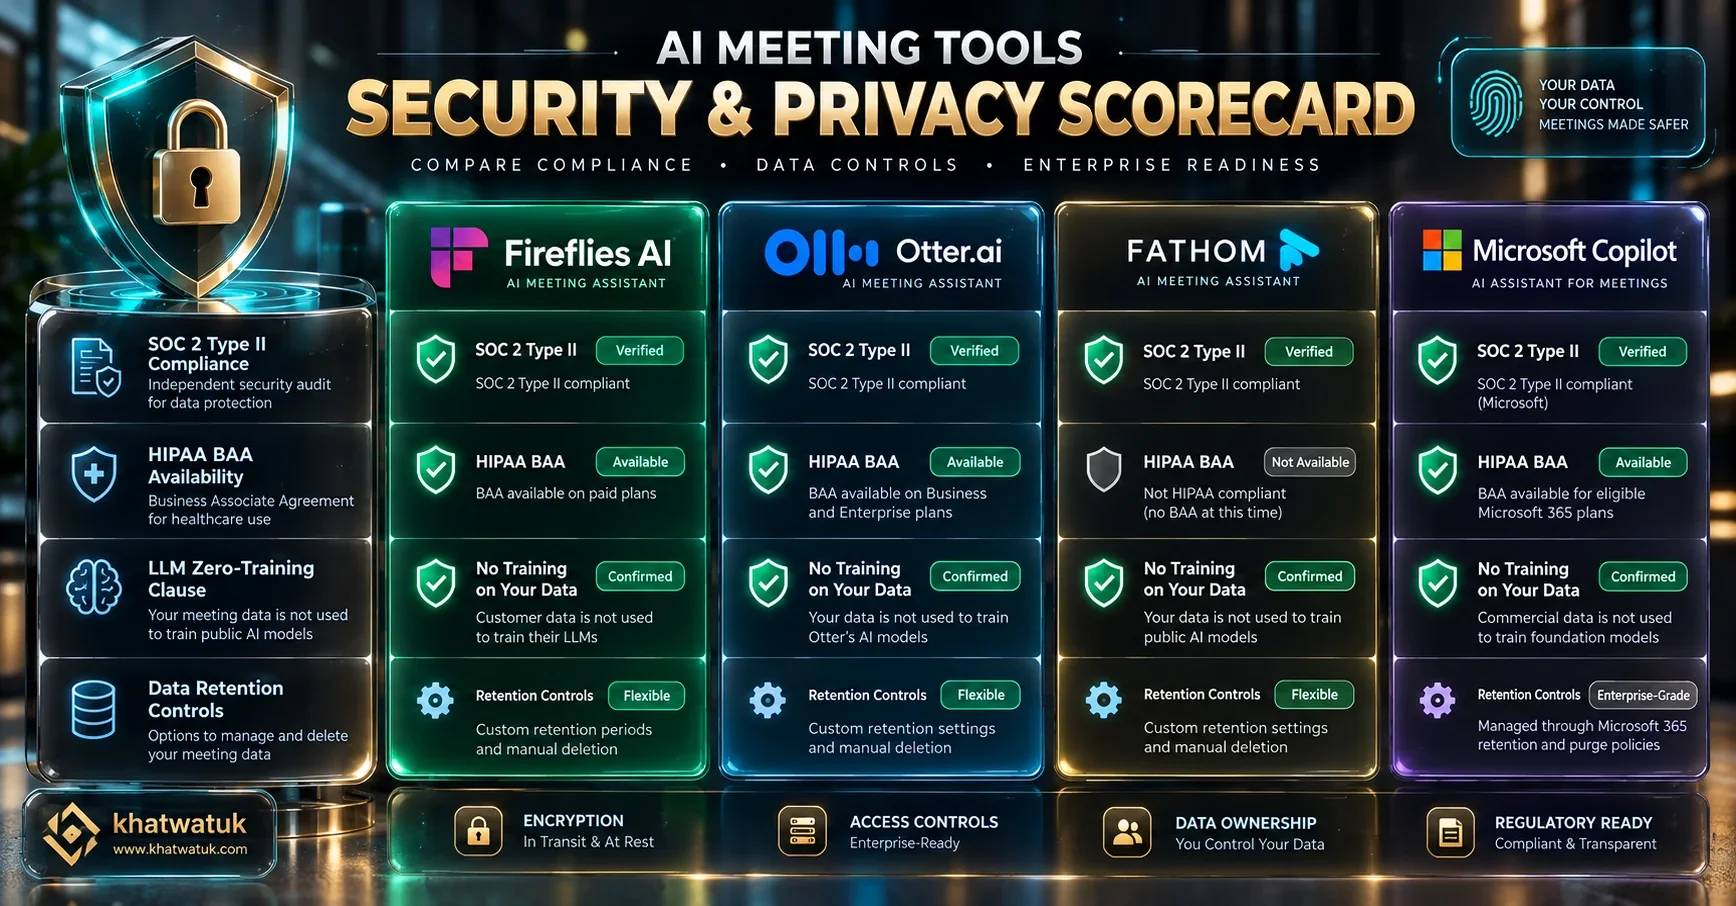
| Platform | SOC2 Certification | HIPAA BAA Available | Zero-Training Clause | Data Encryption | SSO / SCIM |
|---|---|---|---|---|---|
| Fireflies.ai | SOC2 Type II (Annual) | Yes (Enterprise Tier) | 100% Guaranteed | AES-256 / TLS 1.3 | Okta, Entra, SAML |
| Microsoft Copilot | SOC2 Type II, ISO 27001 | Yes (M365 Enterprise) | 100% Guaranteed | BitLocker / TLS 1.3 | Native Entra ID |
| Fathom | SOC2 Type II Certified | No (Limited Healthcare) | 100% Guaranteed | AES-256 / TLS 1.3 | Google / Okta SAML |
| Otter.ai | SOC2 Type II Certified | No (Not Recommended) | Yes (Paid Business Tier) | AES-256 / TLS 1.2+ | SAML SSO Only |
| Krisp AI | SOC2 Type II Certified | Yes (On-Device Filtering) | On-Device Audio Process | AES-256 at Rest | Okta, Azure AD |
The LLM Training Clause: Does Fireflies Train on Your Conversations?
The single greatest security anxiety surrounding generative AI meeting tools is model poisoning and intellectual property leakage into public AI models.
In Fireflies.ai's explicit legal Terms of Service and Data Processing Addendum (DPA), Fireflies provides an unequivocal contractual guarantee: Customer meeting data, spoken audio recordings, and synthesized text transcripts are NEVER used to train, retrain, or fine-tune public foundational AI models (such as OpenAI GPT models or Anthropic Claude).
🔒 Zero-Data Retention API Routing
Fireflies accesses foundational LLMs through specialized enterprise API tiers with zero-data-retention (ZDR) endpoints. When a transcript is routed through an LLM for summary synthesis, the model vendor does not log or persist the payload in cache memory.
Data Encryption Architecture: AES-256 at Rest & TLS 1.3 in Transit
Data security in Fireflies is architected around multi-layered defense in depth:
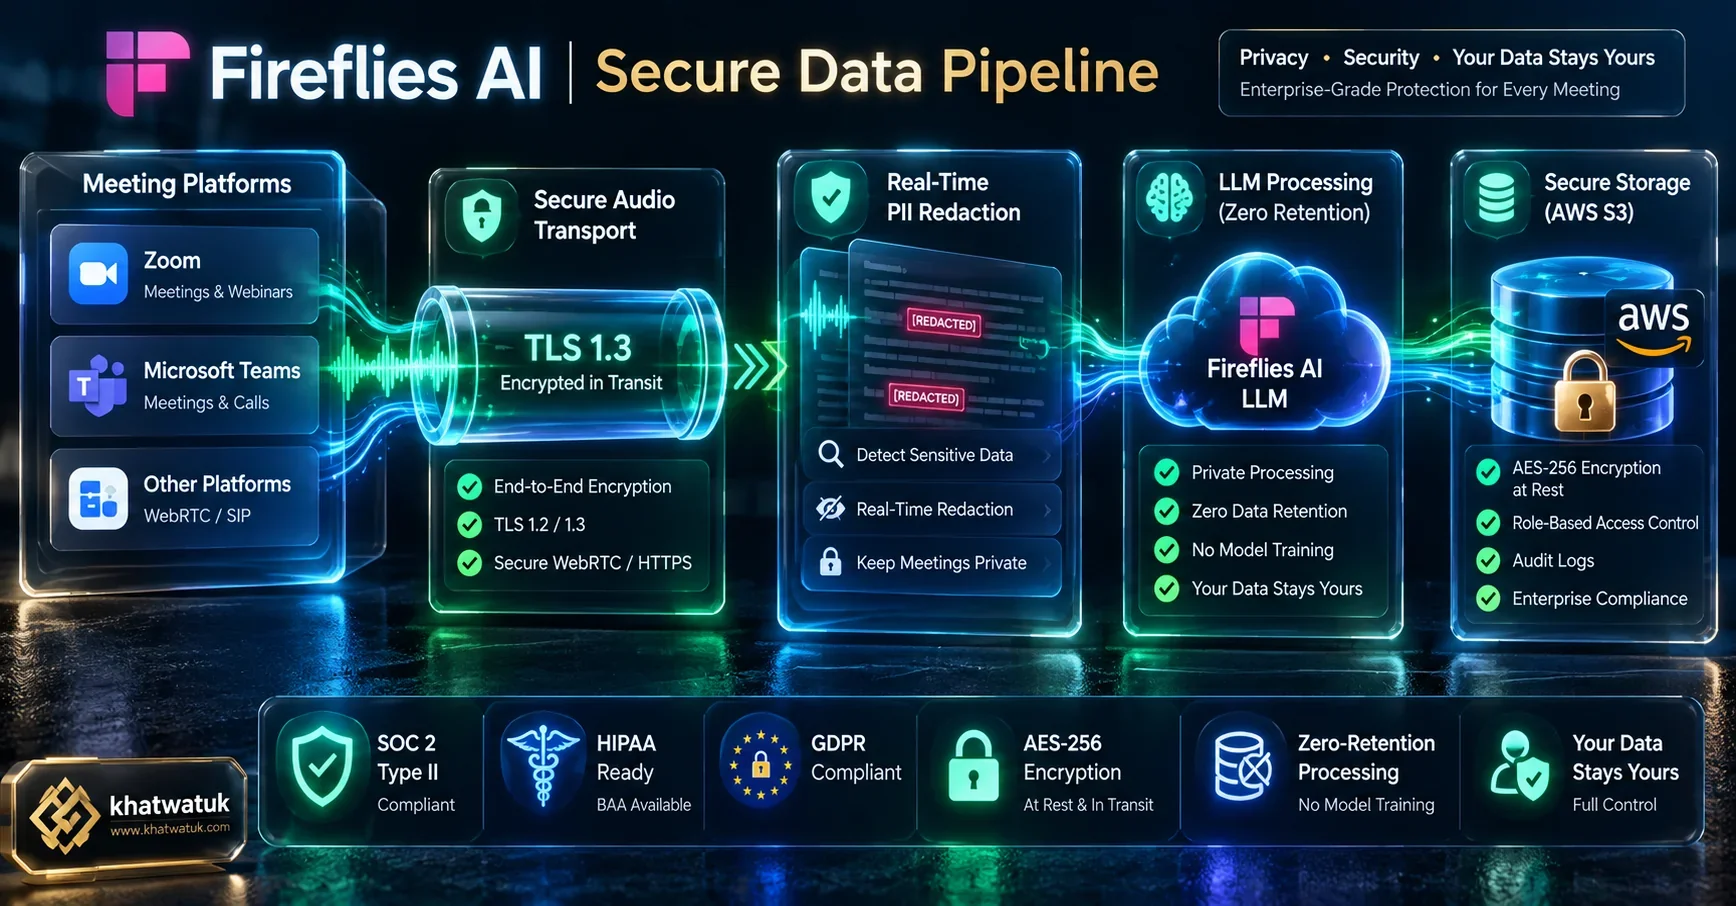
- In-Transit Encryption: All audio streams intercepted from Zoom, Google Meet, or Microsoft Teams travel across TLS 1.3 connections utilizing 256-bit elliptic-curve cryptography. Plaintext HTTP traffic is rejected at the network gateway.
- At-Rest Storage Encryption: Audio files, transcript databases, and AI notes are persisted in Amazon Web Services (AWS S3 and RDS) encrypted with AES-256 via AWS KMS.
- Key Management: Enterprise customers can request Bring-Your-Own-Key (BYOK) configurations, ensuring that only customer administrators possess the cryptographic keys required to decrypt cold archives.
Data Sovereignty & Geographic Storage Options (US, EU, UK)
For European enterprises bound by GDPR Schrems II rulings, transferring corporate audio to United States servers represents a legal compliance hazard.
Fireflies provides dedicated EU data residency options on its Enterprise tier. European organizations can elect to have all meeting audio, user metadata, and transcripts stored exclusively within AWS Frankfurt (eu-central-1) or AWS Dublin (eu-west-1), satisfying cross-border data transfer mandates.
PII Redaction & Automated Sensitive Data Sanitization
During live customer sales or technical support calls, participants routinely recite sensitive credentials, credit card numbers, or social security details.
Fireflies includes an automated Personally Identifiable Information (PII) redaction filter. When activated by team admins, the neural transcription engine automatically masks detected credit card numbers, US social security numbers, passwords, and banking IBAN codes, replacing them with [REDACTED] in both the visual transcript and CRM payloads.
Role-Based Access Control (RBAC), SSO, and SCIM Provisioning
Managing who can listen to confidential executive board meetings versus open engineering syncs requires granular identity management.
- SAML 2.0 Single Sign-On (SSO): Integrate with Okta, Microsoft Entra ID (Azure AD), Google Workspace, or OneLogin with mandatory Multi-Factor Authentication (MFA).
- Automated SCIM Provisioning: Instantly de-provision departing employees. When HR deactivates an employee in Okta, their Fireflies session tokens are instantly revoked, preventing ex-employees from retaining access to meeting archives.
- Granular Privacy Sharing Rules: Admins can enforce global defaults where meetings are only visible to participants who were physically on the calendar invite.
Data Retention Policies & Permanent Purging Controls (GDPR Art. 17)
Keeping unencrypted audio recordings indefinitely creates massive liability in civil litigation and regulatory investigations.
Inside the Fireflies Admin console, security teams can define automatic retention lifecycle rules: auto-delete recordings after 30, 60, or 90 days. Furthermore, when an individual exercises their GDPR Article 17 "Right to be Forgotten", Fireflies provides programmatic APIs to hard-delete all matching voice and text artifacts across databases.
Competitor Security Showdown: Fireflies vs Otter vs Fathom vs Copilot
How does Fireflies compare to its primary competitors from a pure security perspective?
- Fireflies vs Otter.ai: Fireflies is substantially superior for regulated industries. While Otter faced scrutiny in past years over public meeting share links, Fireflies enforces strict domain-matched privacy and offers formal HIPAA BAAs.
- Fireflies vs Microsoft Copilot: Copilot possesses the advantage of staying entirely inside the Microsoft 365 tenant boundary with zero bot ingress. However, for organizations that require cross-platform meetings (Zoom, Meet), Fireflies provides the most hardened third-party architecture.
- Fireflies vs Krisp: Krisp offers the ultimate privacy advantage because its voice isolation runs entirely on-device via local CPU drivers. However, Krisp lacks centralized company-wide searchable intelligence hubs.
12-Month Total Cost of Security Compliance (Standard vs HIPAA)
Evaluating compliance costs requires modeling subscription tiers based on whether your organization requires a formal BAA and custom data retention:
| Deployment Tier | Cost / User / Mo | Compliance Scope | 25 Seats Annual | 100 Seats Annual |
|---|---|---|---|---|
| Business (Standard InfoSec) | $19 | SOC2 Type II, AES-256, Zero-Training | $5,700 | $22,800 |
| Enterprise (Regulated / HIPAA) | $39 | HIPAA BAA, EU Residency, Dedicated VPC | $11,700 | $46,800 |
The Dealbreaker Clause: When InfoSec Teams MUST Reject Fireflies
Despite passing most InfoSec questionnaires, Fireflies should NOT be approved in the following specific circumstances:
- Zero-Bot Corporate Mandate: If your organization's legal policies strictly prohibit any virtual bot attendee from joining meeting rooms, Fireflies cannot function without calendar bot ingress.
- FedRAMP High Mandates: Fireflies is not FedRAMP certified. US defense contractors handling classified government intelligence cannot deploy Fireflies.
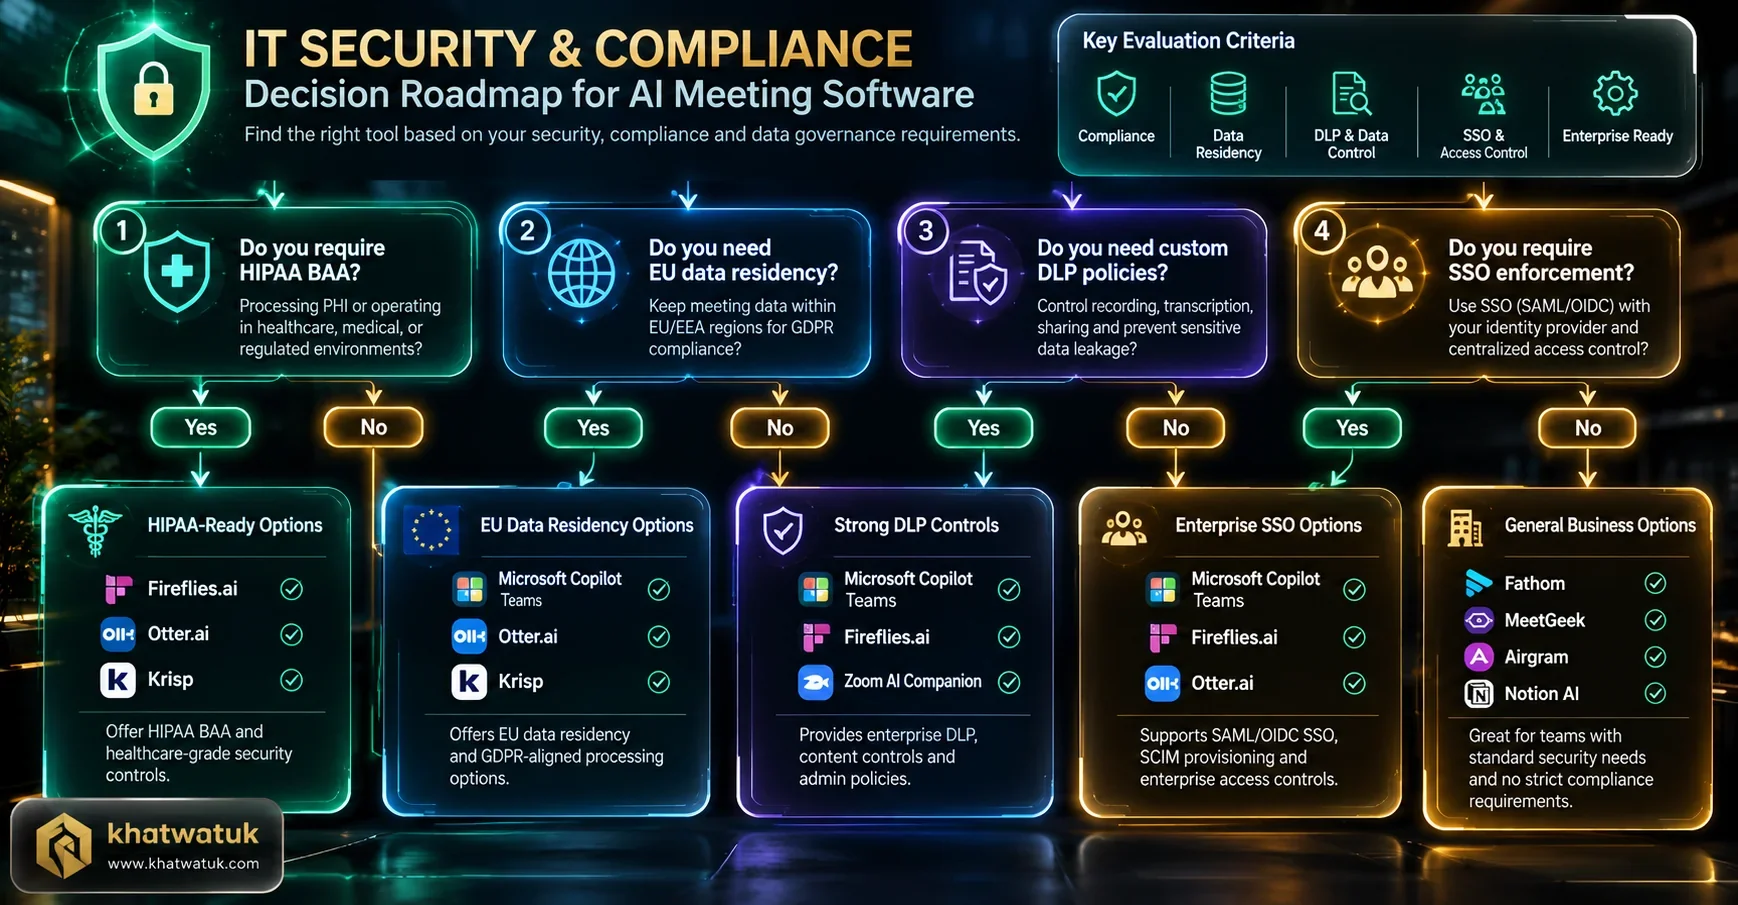
Enterprise IT Vetting Checklist for InfoSec Approvals
Before issuing security clearance for Fireflies, verify these six operational checkpoints:
- Sign the Enterprise DPA: Ensure your legal team executes Fireflies' standard Data Processing Addendum guaranteeing zero model training.
- Execute HIPAA BAA (If Healthcare): Confirm the BAA is counter-signed by Fireflies executive officers before enabling calendar sync on patient-facing accounts.
- Mandate SAML SSO: Enforce login strictly through your corporate identity provider with MFA.
- Configure Internal-Only Bot Rules: Restrict Fred from joining meetings hosted by external third parties until explicit approval is granted.
- Set Data Retention Timers: Automate transcript deletion after 60 or 90 days.
- Activate PII Sanitization: Turn on automatic credit card and SSN redaction across all team workspaces.
Frequently Asked Questions (FAQ)
Is Fireflies AI safe for confidential enterprise business meetings?
Yes. Fireflies is SOC2 Type II and HIPAA compliant, encrypts all audio and transcripts using AES-256 at rest and TLS 1.3 in transit, and contractually guarantees that customer data is never used to train commercial AI models.
Does Fireflies AI train foundational models on my private meetings?
No. Under Fireflies' explicit Data Processing Addendum (DPA), customer meeting audio, transcripts, and notes are never used to train, retrain, or improve foundational AI models from OpenAI, Anthropic, or any third party.
Is Fireflies AI HIPAA compliant?
Yes. Fireflies offers formal Business Associate Agreements (BAAs) for healthcare organizations and medical practices on its Enterprise plan, ensuring all Protected Health Information (PHI) is handled under strict HIPAA controls.
Where does Fireflies store meeting recordings and transcripts?
Fireflies persists data in encrypted Amazon Web Services (AWS) data centers in the United States by default. Enterprise customers can configure dedicated European data residency in AWS Frankfurt or Dublin to comply with GDPR requirements.
Can Fireflies employees listen to my private recorded calls?
No. Fireflies employees do not have routine access to customer meeting recordings or transcripts. Access to customer data is strictly governed by least-privilege role-based permissions, requiring explicit customer authorization for technical support investigations.
Can I automatically redact sensitive credit card numbers and passwords?
Yes. Fireflies includes an automated PII redaction engine that detects and masks credit cards, social security numbers, and credentials, replacing them with redacted placeholders before storing transcripts or pushing data to CRMs.
How do I permanently delete meeting recordings to satisfy GDPR?
Team administrators can delete individual meetings or purge entire workspace histories through the Fireflies dashboard or programmatic REST APIs. Deletion permanently erases the audio file and transcripts from primary storage and backup servers.
Is Fireflies safer than Otter.ai?
Yes. Fireflies provides stronger enterprise security controls than Otter.ai, including formal HIPAA BAAs, dedicated EU data sovereignty hosting, and stricter domain-level meeting participant sharing permissions.
Deploy Enterprise-Grade Meeting Intelligence Safely
Protect your company's intellectual property while empowering teams with automated notes, CRM syncing, and conversational search.
Review Fireflies Enterprise Security → Explore Fathom SOC2 →